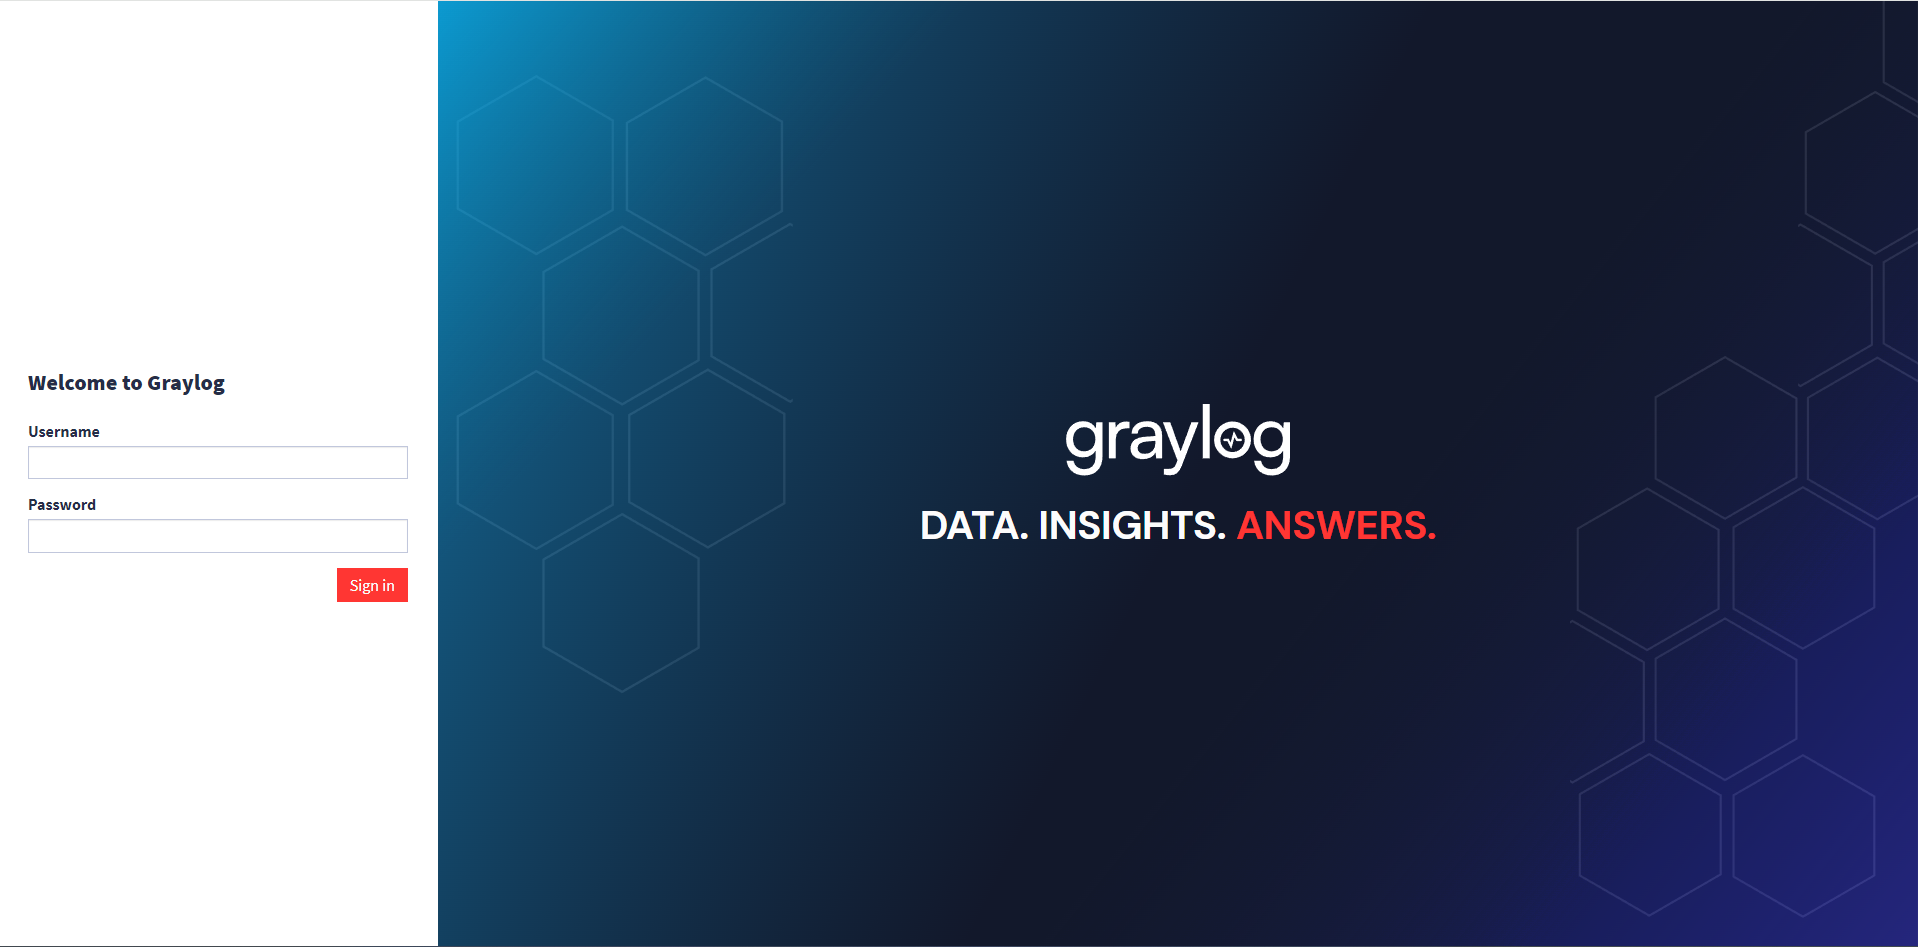
When your Graylog installation is complete and you have started the Graylog service, you will likely want to sign on to the web interface, which is primarily how you use the Graylog application. After completing the initial preflight login, default access to the interface is found via a compatible browser at https://<graylog-server>:9000/.
This article explains how to adjust configurations and access the Graylog web interface.
Prerequisites
Before proceeding, ensure that the following prerequisites are met:
-
You must be a Graylog administrator to configure the web interface and log in for the first time.
-
JavaScript must be enabled.
-
You must access the interface via a compatible browser. Here are the supported browsers for Graylog 7.2 along with the operating systems on which each browser is supported:
Browser
OS
Supported Versions Chrome
Windows, OS X, Linux
Latest plus two previous releases
Firefox
Windows, OS X, Linux
Latest plus two previous releases
Safari
OS X
Latest plus two previous releases
Highlights
The following highlights provide a summary of the key takeaways from this article:
-
Use
https://<graylog-server>:9000/to reach the web interface after installation. -
Initial login uses credentials found in the initial log file; do not use your permanent password for the preflight login!
-
Adjust settings like
http_bind_address,http_publish_uri, andhttp_external_uriin the server configuration files. -
The interface URL is determined by the
X-Graylog-Server-URLheader, thenhttp_external_uri, thenhttp_publish_uri, and finally the default bind address. -
Ensure proper access and SSL setup when using load balancers or reverse proxies.
Configuration Settings
During installation, you can set the primary configuration properties to access the web interface. If the default settings do not work for your environment, you can adjust settings in the Graylog server configuration file. In addition to the installation properties, the following table includes additional properties that affect the web interface. You can configure these properties as needed:
|
Setting |
Default |
Explanation |
|---|---|---|
|
|
127.0.0.1:9000
|
The network interface used by the Graylog HTTP interface. |
|
|
If not set, |
The HTTP URI of this Graylog node, which is used to communicate with the other Graylog nodes in the cluster and by all clients using the Graylog web interface. |
|
|
If not set, |
The public URI of Graylog, which is used by the Graylog web interface to communicate with the Graylog REST API. |
|
|
|
This setting is necessary for JavaScript clients accessing the server directly. If disabled, modern browsers are not able to retrieve resources from the server. |
|
|
|
Uses compression to serve web interface assets to reduce overall round-trip times. |
|
|
|
Sets the maximum size of the HTTP request headers in bytes. |
|
|
|
Sets the size of the thread pool used exclusively for serving the HTTP interface. |
Connect to the Graylog Server
The web interface fetches information from the REST API of the Graylog server. Therefore, the web interface needs to connect to the server using HTTP(S). You have several ways you can define the connection between the web interface and the Graylog server. The URI used by the web interface is determined in the following order:
- If the HTTP(S) client going to the web interface port sends a
X-Graylog-Server-URLheader that contains a valid URL, then this value overrides everything else. - If
http_external_uriis defined in the Graylog configuration file,server.conf, this value is used if the previous condition is not met. - If
http_publish_uriis defined in the Graylog configuration file, this value is used if the previous conditions are not met. - If none of the above are defined,
https://$http_bind_addressis used.
Connection Example
For example, setting http_bind_address to 10.0.0.1:9000 configures the Graylog server with the following URLs:
- Web interface:
https://10.0.0.1:9000/ - REST API:
https://10.0.0.1:9000/api/
Preflight Login
When you sign on to Graylog for the first time, you must use the initial credentials for the Graylog web interface, which can be found in the log file after first starting the Graylog service.
graylog-1   |                                                              ---
graylog-1   |                                                              ---
graylog-1   |                                                              ---
graylog-1   |     ########  ###   ######### ##########   ####         #### ---         .----               ----
graylog-1   |   ###############   ###################### #####       ####  ---      ------------       .----------- --
graylog-1   |  #####     ######   #####              #### ####      ####   ---     ---        ---     ---        -----
graylog-1   | ####         ####   ####       ############  ####     ####   ---    --           ---   ---           ---
graylog-1   | ###           ###   ####     ##############   ####   ####    ---   ---            --   --             --
graylog-1   | ####         ####   ####    ####       ####    #### ####     ---   ---            --   --            .--
graylog-1   | #####       #####   ####    ####       ####     #######      ---    ---          ---   ---           ---
graylog-1   |  ################   ####     ##############     ######-       --     ----      ----      ---       -----
graylog-1   |    ##############   ####      #############      #####        -----   -----------         ----------  --
graylog-1   |              ####                                ####                                                ---
graylog-1   | #####       ####                                ####                                     -          .--
graylog-1   |   #############                                ####                                     -----     ----
graylog-1   |      ######                                   ####                                          -------
graylog-1   |
graylog-1   | ========================================================================================================
graylog-1   |
graylog-1   | It seems you are starting Graylog for the first time. To set up a fresh install, a setup interface has
graylog-1   | been started. You must log in to it to perform the initial configuration and continue.
graylog-1   |
graylog-1   | Initial configuration is accessible at 0.0.0.0:9000, with username 'admin' and password 'ghWgeIAkKl'.
graylog-1   | Try clicking on http://admin:ghWgeIAkKl@0.0.0.0:9000
graylog-1   |
graylog-1   | ========================================================================================================
graylog-1   |
To view your initial password and the instructions included in the log file, enter the following command:
tail /var/log/graylog-server/server.logThese credentials are only for your initial preflight sign on, where you configure Data Node and set up certificates. You must use these credentials for preflight rather than your chosen administrator password! This step ensures that, if you have not yet set up HTTPS to connect to Graylog, your administrative password is not compromised.
For subsequent sign ons, you can use the password_secret you selected during installation.
password_secret when logging in to Graylog for the first time. This WILL NOT work! You need to locate and utilize the credentials in the initial log file.
Access the Web Interface
After you complete your preflight login, you can access the web interface with your regular credentials:
-
Open a compatible browser and navigate to the URL
https://xxx.xxx.xxx.xxx:9000. Substitute the IP address of your Graylog server. -
Log in as an admin and use the password secret you created when you installed Graylog.
Get Started with the Web Interface
After you log in to the web interface, Graylog opens the Welcome page. A new installation shows a guided view that helps you ingest your first logs into Graylog. After that, the Welcome page switches to a standard view that fills in with information specific to your work in Graylog.
Welcome Page on a New Installation
On a new installation, Graylog has not received any log data, so there are no saved searches, dashboards, or recent activity to show. Instead, the Welcome page offers two ways to begin ingesting data:
-
Enroll Collector: Opens the System > Collectors page so you can install a Graylog Collector. You enroll this lightweight agent and manage its configuration centrally from Graylog.
-
Set up Input: Opens the System > Inputs page to create an input, a network listener on your Graylog nodes that receives logs over protocols such as Syslog or GELF.
Resource links to a quick start guide that walks you through your first search, a video on enrolling a Collector, and the Graylog Community Forum are provided on the Welcome page.
The guided view appears only on new installations. If you upgrade an existing installation, Graylog skips the guided view and shows the standard Welcome page.
Standard Welcome Page
After the guided view ends, or if your installation was upgraded, the Welcome page shows content based on your activity in Graylog.
At the top of the Welcome page, the Overview section summarizes recent activity in your environment. The General view charts your top message sources over the last day. If you have a Graylog Security license, you can use the toggle in the upper right to switch to the Security view. That view shows key security metrics, such as alert counts, high-risk assets, and investigations, along with event and alert trends.
The Search and Usage section includes the following information:
-
Favorite Items: An overview of saved searches and dashboards that you have marked as favorite items.
-
Recent Activity: A list of recent actions by other Graylog users, including newly created content or content shared with you.
-
Last Opened: A list of your most recently viewed saved searches and dashboards so you can resume your latest journey if desired.
On your initial log on, these sections are blank, but they are populated with current information as you work in Graylog.
In addition, the following sections are updated by Graylog to provide you with the current, useful information:
-
News: Includes links to recent data security and administration articles.
-
Releases: Lists the most recent release announcements for Graylog.
Adjust the Web Interface for Load Balancers and Proxies
If your environment is set up to run a load balancer or reverse proxy in front of Graylog, you must ensure that:
- The HTTP port of the load balancer/reverse proxy is accessible for clients
- The HTTP address for the Graylog server is properly set so it is resolvable and accessible for the load balancer/reverse proxy.
- If you use SSL, your certificates must be valid and trusted by your clients.
Load Balancer and Proxy Examples
In the follow examples, we demonstrate several scenarios in which your configuration settings must be adjusted for access to the interface. For these examples, we assume the following:
- Your Graylog server configuration contains
http_bind_address = 127.0.0.1:9000. - The hostname for the setup is
graylog.example.org. - The IP address for that hostname is
192.168.0.10.
Layer 3 Load Balancer (Forwarding TCP Ports)
- Configure your load balancer to forward connections going to
192.168.0.10:80127.0.0.1:9000. - Start the Graylog server as usual.
- Access the web interface on
https://graylog.example.org.
NGINX
Proxy web interface and API traffic using HTTP
server
{
    listen 80 default_server;
    listen [::]:80 default_server ipv6only=on;
    server_name graylog.example.org;

    location / {
      proxy_set_header Host $http_host;
      proxy_set_header X-Forwarded-Host $host;
      proxy_set_header X-Forwarded-Server $host;
      proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
      proxy_set_header X-Graylog-Server-URL http://$server_name/;
      proxy_pass       http://127.0.0.1:9000;
    }
}
NGINX can be used for SSL termination. You would only need to modify the server listen
If you are deploying multiple Graylog nodes, you can use HTTPS/SSL to connect to the Graylog nodes and use HTTPS/SSL on NGINX. Note that configuration for TLS certificates, keys, and ciphers is omitted from the sample configurations below.
Proxy web interface and API traffic using HTTPS (TLS)
server
{
    listen      443 ssl http2;
    server_name graylog.example.org;
    # <- your SSL Settings here!

    location /
    {
      proxy_set_header Host $http_host;
      proxy_set_header X-Forwarded-Host $host;
      proxy_set_header X-Forwarded-Server $host;
      proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
      proxy_set_header X-Graylog-Server-URL https://$server_name/;
      proxy_pass       http://127.0.0.1:9000;
    }
}
If you want to serve several different applications under one domain name, you can also accessthe Graylog web interface using a path prefix.
Proxy web interface and API traffic under a path prefix using HTTP
server
{
    listen 80 default_server;
    listen [::]:80 default_server ipv6only=on;
    server_name applications.example.org;

    location /graylog/
    {
      proxy_set_header Host $http_host;
      proxy_set_header X-Forwarded-Host $host;
      proxy_set_header X-Forwarded-Server $host;
      proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
      proxy_set_header X-Graylog-Server-URL http://$server_name/graylog/;
      rewrite          ^/graylog/(.*)$  /$1  break;
      proxy_pass       http://127.0.0.1:9000;
    }
}
This makes your Graylog setup available under the following URLs:
- Web interface:
https://applications.example.org/graylog/ - REST API:
https://applications.example.org/graylog/api/
Apache httpd 2.x
Proxy web interface and API traffic using HTTP
<VirtualHost *:80>
    ServerName graylog.example.org
    ProxyRequests Off
    <Proxy *>
        Order deny,allow
        Allow from all
    </Proxy>

    <Location />
        RequestHeader set X-Graylog-Server-URL "http://graylog.example.org/"
        ProxyPass http://127.0.0.1:9000/
        ProxyPassReverse http://127.0.0.1:9000/
    </Location>

</VirtualHost>
Proxy web interface and API traffic using HTTPS (TLS)
<VirtualHost *:443>
    ServerName graylog.example.org
    ProxyRequests Off
    SSLEngine on
    # <- your SSL Settings here!

    <Proxy *>
        Order deny,allow
        Allow from all
    </Proxy>

    <Location />
        RequestHeader set X-Graylog-Server-URL "https://graylog.example.org/"
        ProxyPass http://127.0.0.1:9000/
        ProxyPassReverse http://127.0.0.1:9000/
    </Location>

</VirtualHost>
HAProxy 1.6
Proxy web interface and API traffic using HTTP
frontend http
    bind 0.0.0.0:80

    option forwardfor
    http-request add-header X-Forwarded-Host %[req.hdr(host)]
    http-request add-header X-Forwarded-Server %[req.hdr(host)]
    http-request add-header X-Forwarded-Port %[dst_port]
    acl is_graylog hdr_dom(host) -i -m str graylog.example.org
    use_backend     graylog if is_graylog

backend graylog
    description     The Graylog Web backend.
    http-request set-header X-Graylog-Server-URL http://graylog.example.org/
    use-server graylog_1
    server graylog_1 127.0.0.1:9000 maxconn 20 check
Multiple backends (roundrobin) with Health-Check (using HTTP)
frontend graylog_http
    bind *:80
    option forwardfor
    http-request add-header X-Forwarded-Host %[req.hdr(host)]
    http-request add-header X-Forwarded-Server %[req.hdr(host)]
    http-request add-header X-Forwarded-Port %[dst_port]
    acl is_graylog hdr_dom(host) -i -m str graylog.example.org
    use_backend     graylog

backend graylog
    description     The Graylog Web backend.
    balance roundrobin
    option httpchk HEAD /api/system/lbstatus
    http-request set-header X-Graylog-Server-URL http://graylog.example.org/
    server graylog1 192.168.0.10:9000 maxconn 20 check
    server graylog2 192.168.0.11:9000 maxconn 20 check
    server graylog3 192.168.0.12:9000 maxconn 20 check
Further Reading
Explore the following additional resources and recommended readings to expand your knowledge on related topics: